AI Data Risk Management: Securing Prompts and Conversations
In the era of generative AI, employees inadvertently sharing sensitive information with large language models has become a top-tier threat. To implement effective AI data risk management, enterprises must shift from purely technical perspectives to a rigorous operational governance framework. This article focuses on Prompt security serves as the as a practical implementation direction for businesses. This article focuses on conversation governance as a practical implementation direction for businesses.
AI Data Risk Management: Securing
The Challenge of Shadow AI
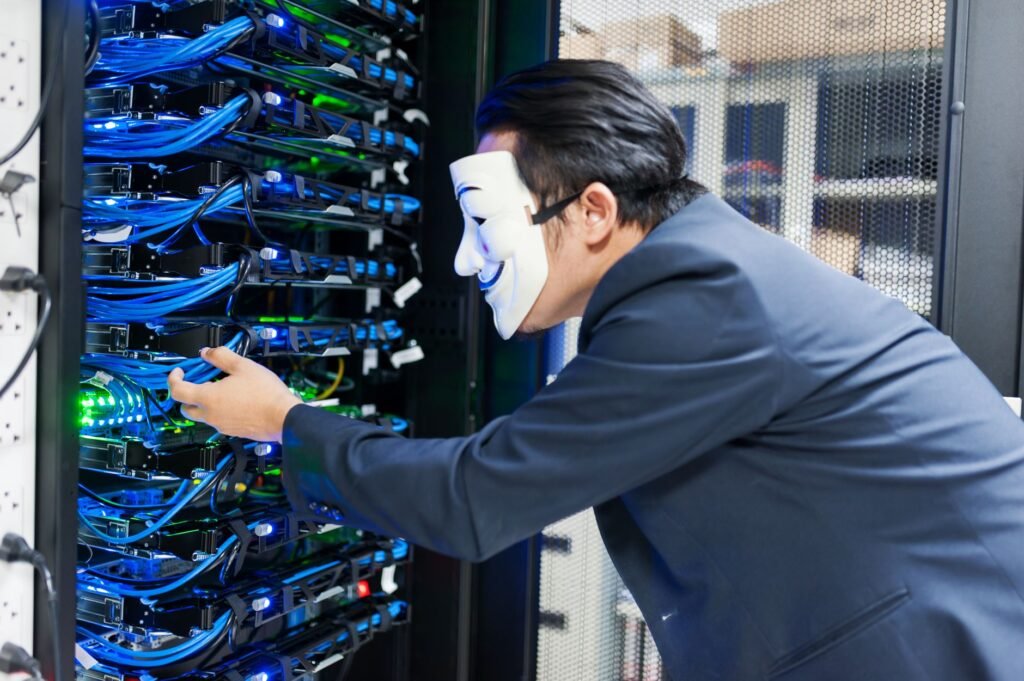
The rise of ‘Shadow AI’—where employees use public AI tools without IT approval—creates massive security gaps. When data is entered into a prompt, it risks being stored in conversation logs and used for model training. Mastering AI data risk management is no longer just a technical task; it is a critical requirement for protecting organizational intellectual property.
Context: Aligning with NIST Standards
Drawing from the NIST AI Risk Management Framework, organizations should integrate security policies throughout the AI lifecycle. Rather than outright bans, companies should implement automated guardrails. Prompt security serves as the first line of defense, preventing the input of personally identifiable information (PII) or financial data into unvetted platforms.
Solution Analysis: Governance Pillars
To achieve sustainable AI data risk management, businesses should focus on three pillars:
- Data Classification: Clearly define what information is permitted in prompts.
- Access Control: Use role-based access to limit interactions with AI tools.
- Real-time Monitoring: Deploy content filtering to ensure prompt security remains consistent.
Furthermore, conversation governance is often overlooked. Conversation history must be periodically purged or stored in secure, isolated environments, separate from the AI provider’s training databases. Effective conversation governance ensures that past interactions do not become future liabilities.
Practical Recommendations
Organizations should treat AI data risk management as an ongoing process. By combining monitoring technology with employee awareness, firms can leverage AI while maintaining strict data integrity. Implementing robust prompt security protocols helps mitigate the risk of data poisoning and unauthorized leakage.
Implementation Checklist
- Audit all AI tools currently in use to eliminate Shadow AI.
- Update prompt security policies to align with current compliance standards.
- Clear conversation history on shared AI accounts regularly.
- Review access permissions for AI tools integrated with internal data.
- Conduct training on the risks of sharing sensitive data via AI prompts.
With AI Data Risk Management: Securing, businesses can standardize governance, reduce manual work, and improve data control.
Prompt security serves as the
Conversation governance
Conclusion
Successful AI data risk management requires a blend of automated controls and human oversight. By prioritizing conversation governance and prompt integrity, enterprises can safely navigate the complexities of generative AI.
References
- AI Risk Management Framework | NIST
- Artificial Intelligence Risk Management Framework (AI …
- NIST AI Risk Management Framework (AI RMF) – Palo Alto Networks
- Privacy Framework | NIST
- Security considerations for data in generative AI – AWS Prescriptive Guidance
- Prompt Security | SentinelOne AI Security Platform
Image credit: Photo by AlphaTradeZone on Pexels – Pexels.
- Automating Customer Ticket Routing with AI: A Guide for Enterprises
- Managing departing employee data in OneDrive: A standard business process
- Mastering Customer Data Across Disparate Systems: Solving the Fragmentation Puzzle
- Managing Shadow AI: How to Control Unsanctioned AI Usage
- Centralized IT asset management for multi-department enterprises